Network segmentation
FortiFlow2
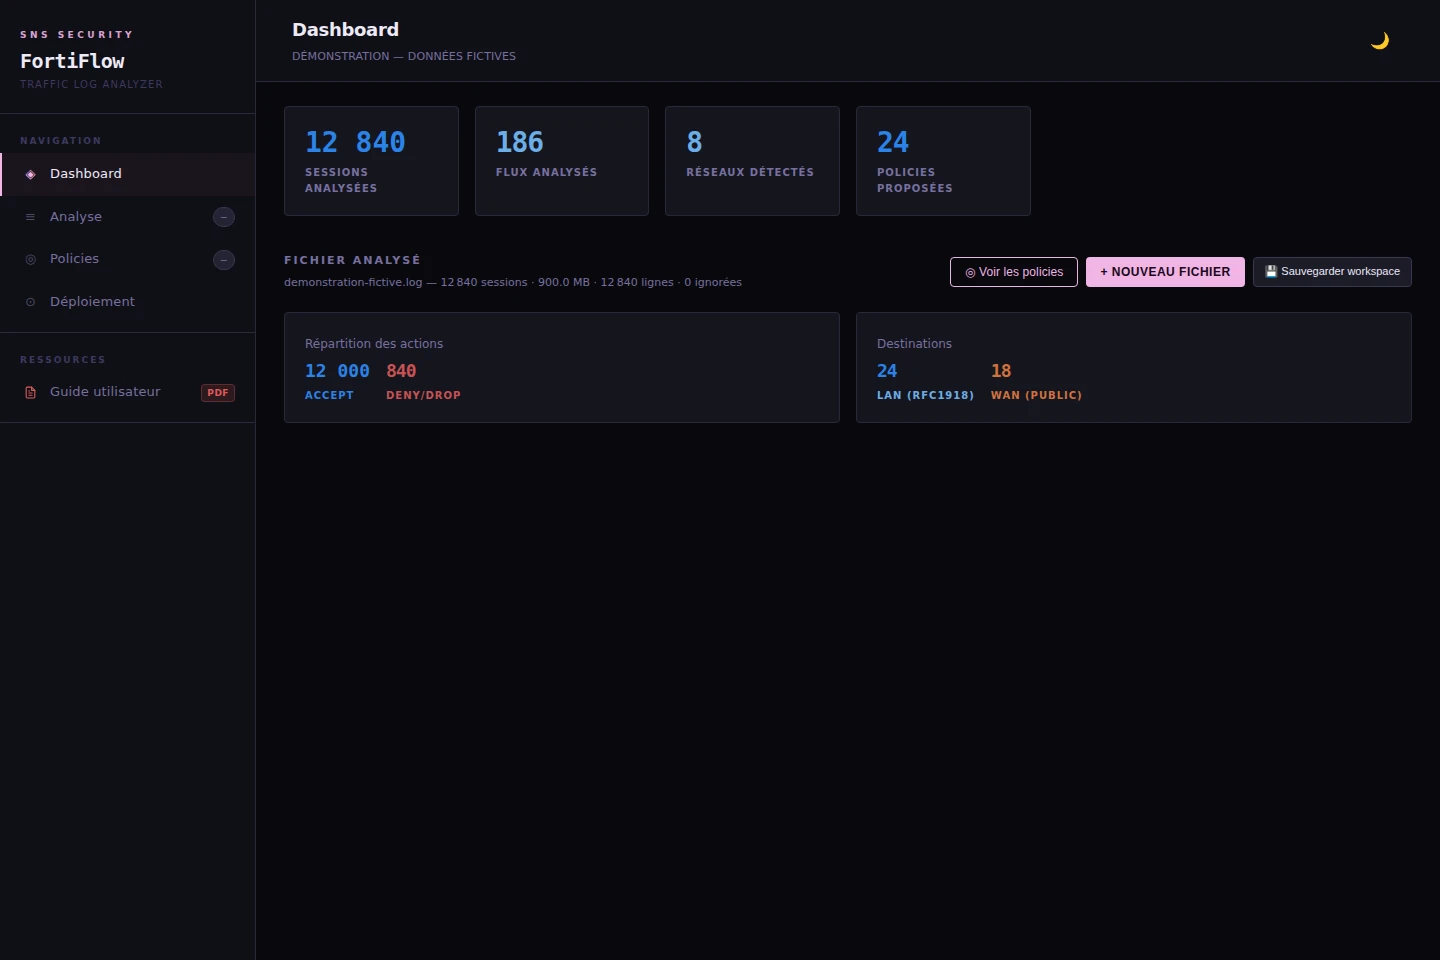
Turn traffic logs into understandable FortiGate policies, with checks before generation.
View source- Analyse observed traffic
- Understand policy grouping
- Check before generating
The need
Logs show which machines communicate. On their own, they do not tell you which firewall policies to create. Grouping too broadly can allow communication that has never been observed.
My role
I define the requirements from my network experience, set the security rules and lead the design. I check proposed policies against test scenarios before command generation.
The design
- Trace each proposed policy back to observed traffic.
- Distinguish exact grouping from policies that allow additional traffic.
- Leave ambiguous cases to the engineer.
- Use the same checks for preview and command generation.
- 01Import logs
- 02Review traffic
- 03Check proposals
- 04Generate commands
What the tool delivers
The tool connects traffic analysis with policy preparation. Each proposal remains linked to the observations behind it, so the engineer can understand and check the result.
Scope & limitations
FortiFlow2 is still under validation. It prepares proposals and commands; the engineer decides whether a policy should be applied.
Validation notes
For the version documented in September 2026, 310 tests and the full analysis-to-generation workflow passed. Balanced and Compact strategies add no traffic in the reference scenario. Final review remains outstanding before pre-deployment use with engineer approval.